When securing a server environment, most administrators mistakenly rely entirely on application-layer software. They install heavy firewall plugins, assuming their application is safe, while completely ignoring the server’s HTTP response headers. This oversight leaves the site highly vulnerable to Clickjacking, MIME-type sniffing, and Cross-Site Scripting (XSS).
To truly lock down your infrastructure, you must deploy strict WordPress HTTP security headers. These are server-level directives that instruct the visitor’s browser exactly how to behave before the website even loads. By shifting your cybersecurity perimeter to the edge of the server, you block malicious scripts from executing and prevent unauthorized framing without taxing your PHP workers or database.
The Plugin Illusion: Why Server-Level Fortification is Better
A plugin can only protect your site after WordPress core and PHP have initialized. If a sophisticated XSS payload bypasses your plugin’s filters, it executes directly in the user’s browser.
By configuring WordPress HTTP security headers in your server block (Nginx) or .htaccess file (Apache), you remove the application layer from the equation. The web server dictates the rules. If an attacker tries to embed your admin dashboard into a fake iframe to execute a Clickjacking attack, the browser reads your X-Frame-Options header and instantly refuses to render the page—stopping the attack cold before WordPress is even aware it happened.
This interactive configuration tool demonstrates how adding strict security headers actively blocks common browser-based vulnerabilities:
Key insight: A properly configured Content-Security-Policy (CSP) is the single most effective defense against unauthorized script execution, but it requires careful tuning to avoid breaking legitimate third-party assets.
The Execution: Deploying the Code Blocks
To harden your WordPress architecture, you must inject these headers directly into your server configuration files. Below are the exact code blocks required for both Nginx and Apache to deploy a robust baseline of WordPress HTTP security headers.
1. Strict-Transport-Security (HSTS)
HSTS forces web browsers to interact with your server exclusively over secure HTTPS connections, preventing man-in-the-middle protocol downgrade attacks.
2. X-Content-Type-Options
Setting this to nosniff prevents browsers from trying to guess the MIME type of a file. This stops attackers from disguising executable scripts as harmless image or text uploads.
3. X-Frame-Options
Setting this to SAMEORIGIN guarantees that your content cannot be embedded into an iframe on a malicious third-party domain, completely eliminating Clickjacking threats.
4. Content-Security-Policy (CSP)
A strict CSP restricts where resources (like JavaScript, fonts, and images) can be loaded from. (Note: The example below is a strict baseline. You will need to add your specific CDN or external script domains to prevent breaking your site).
Nginx Implementation (nginx.conf)
Open your server block configuration and add the following lines within the server {} context:
add_header Strict-Transport-Security “max-age=31536000; includeSubDomains; preload” always;
add_header X-Content-Type-Options “nosniff” always; add_header X-Frame-Options “SAMEORIGIN” always;
add_header X-XSS-Protection “1; mode=block” always;
add_header Content-Security-Policy “default-src ‘self’; script-src ‘self’ ‘unsafe-inline’; style-src ‘self’ ‘unsafe-inline’; img-src ‘self’ data: https:;” always;
Apache Implementation (.htaccess)
Open your .htaccess file located in the WordPress root directory and append the following directives using the mod_headers module:
<IfModule mod_headers.c>
    Header always set Strict-Transport-Security “max-age=31536000; includeSubDomains; preload”
    Header always set X-Content-Type-Options “nosniff”
    Header always set X-Frame-Options “SAMEORIGIN”
    Header always set X-XSS-Protection “1; mode=block”
    Header always set Content-Security-Policy “default-src ‘self’; script-src ‘self’ ‘unsafe-inline’; style-src ‘self’ ‘unsafe-inline’; img-src ‘self’ data: https:;”
</IfModule>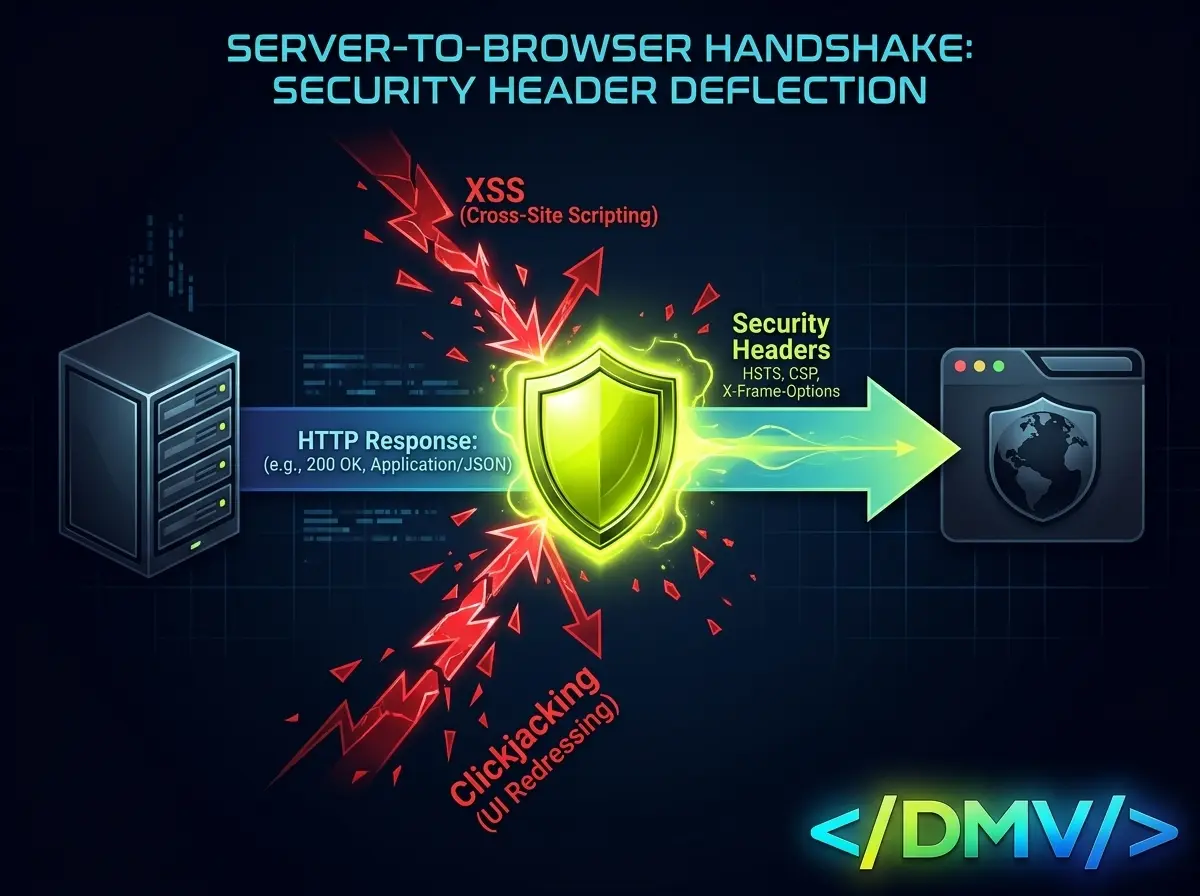
Frequently Asked Questions
[lux_faq htag="h3" open="first" style="card"]
Q:What are HTTP security headers in WordPress?
A:HTTP security headers are directives sent by your web server to a user’s browser before the website even loads. They explicitly instruct the browser on how to behave, automatically blocking malicious scripts, preventing the site from being embedded in fake iframes, and enforcing secure HTTPS connections.
Q:Do WordPress HTTP security headers replace security plugins?
A:No, they complement them. While server-level headers handle edge fortification (blocking XSS and framing), you still need a lightweight plugin or firewall to manage brute-force login attempts, malware scanning, and two-factor authentication.
Q:How do I test if my WordPress HTTP security headers are working?
A:You can verify your configuration by scanning your domain using free online tools like SecurityHeaders.com or the Mozilla Observatory. These tools will grade your setup and flag any missing critical directives.
Q:What happens if my Content-Security-Policy (CSP) is too strict?
A:If your CSP is too restrictive, it will block legitimate resources. For example, if you use Google Analytics or a third-party chat widget, a strict 'self' policy will block their scripts from loading, breaking their functionality on your frontend. You must whitelist trusted domains in your CSP string.
Q:Are HTTP security headers good for SEO and Answer Engine Optimization (AEO)?
A:Yes. Search engines and AI crawlers prioritize secure, trustworthy environments. A properly secured site utilizing HSTS and avoiding mixed-content warnings signals strong administrative maintenance, which acts as a positive ranking factor for modern indexers.
[/lux_faq]
Zero-Trust Infrastructure
Cybersecurity is not about finding the perfect plugin; it is about building a zero-trust architecture from the ground up. By deploying strict WordPress HTTP security headers in your Apache or Nginx configuration, you dictate the terms of engagement before malicious traffic can even interact with your application layer. Audit your response headers today and close the door on browser-based exploits.
